
vCISO AND GRC SOFTWARE FOR MSPs AND MSSPs
Cybrance is the vCISO software that turns security gaps into client decisions
Use our suite of global frameworks to build your clients’ risk program. Identify gaps and show what each means for their business. Build a Plan of Action (POAM) that meets their need and budget.
Cybrance by vCIOToolbox runs all your advisory services from one platform, so security is a part of every touchpoint.
Clients like to talk about security.
They don’t like to buy it.
Security proposals rarely stall because clients don’t care. They stall because nobody took the time to show them the ‘Why”.
Why now? What happens if left alone?
A list of findings won’t close that gap. The MSPs who win show clients where the gaps are, what each one means for the business, and how the plan prevents a loss that would cost far more than the protection.
That’s the difference between a vendor with a quote and an advisor with a plan.
From security risk assessment to audit-ready, in one console
Assess
Pick a framework template from our catalog, including CIS, NIST, ISO, and more, and start the review. Capture every finding in one platform across every client. Say goodbye to spreadsheets
Explain the impact
Show the business impact and likelihood of each finding, from downtime to revenue loss to reputational damage, so clients understand the risk in their own terms.
Plan the fix
Build a remediation plan based on your findings, include evidence, and in your POAM, build a budget and prioritize each option with the client to build your optimal remediation plan.
Prove progress
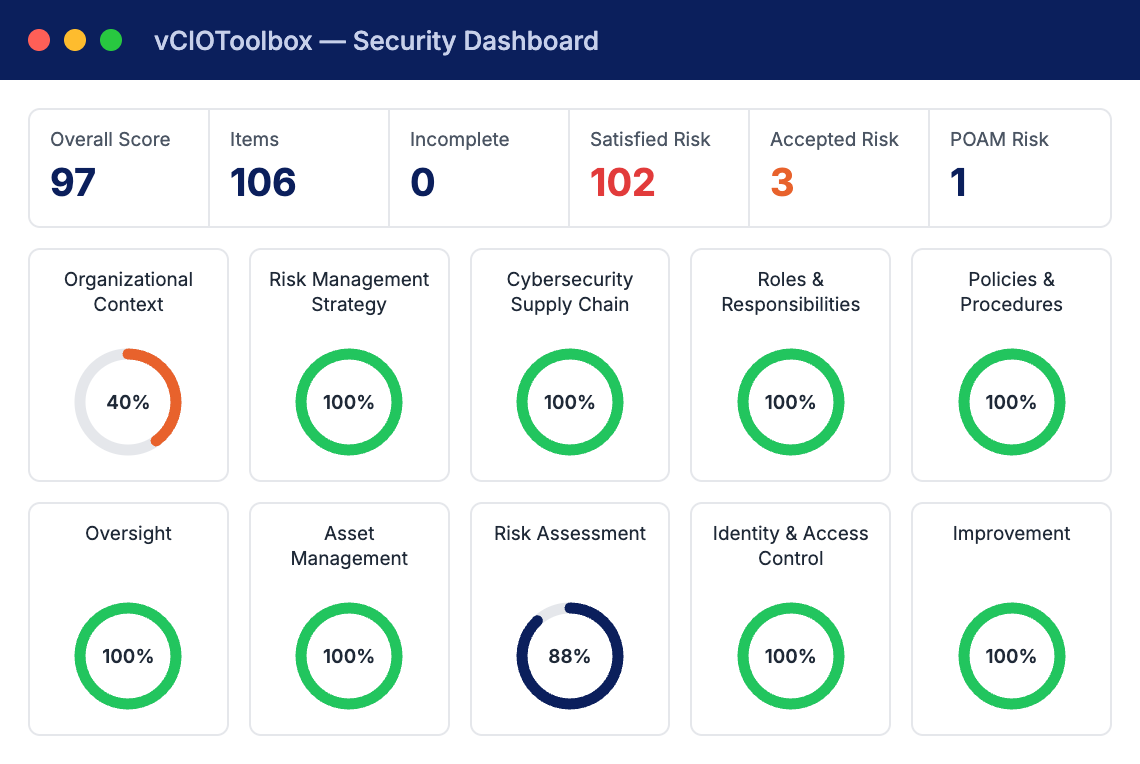
A vCISO program is a continual improvement process. Scoring and trend reports track posture over time, and audit-ready reports help compliance officers and auditors find what they need quickly.
Assess clients against the frameworks they answer to
vCIOToolbox supports 30+ security, regulatory, and governance frameworks, so you can meet each client where they are, whether or not they have a formal compliance requirement
Cybersecurity
NIST Cybersecurity Framework (CSF 2.0), NIST 800-171, CMMC, IASME Cyber Essentials, and CyberSecure Canada. NIST assessments support maturity levels, so you can move clients forward in practical stages.
Regulatory compliance
HIPAA, ISO 27001/27002, GDPR, and others. Prepare clients for audits and examinations with a remediation plan that includes evidence and budget.
IT Governance
COBIT from ISACA, to show the controls that support your clients’ compliance objectives.
vCISO and vCIO in one platform
Standalone vCISO platforms stop at the assessment. In vCIOToolbox, findings become recommendations, recommendations become roadmap items with budgets, and progress shows up in every QBR. Your vCIO and vCISO work from the same data and tell each client one consistent story.
Risk register. Track and score each client’s risks in one place.
Third-party risk. Assess the vendors and suppliers your clients depend on.
Policies and evidence. Keep what auditors ask for alongside the findings it supports.
Program dashboard. See posture and history across every client.
COMPLIANCE AS A SERVICE
Build a compliance practice, not a one-time project
A single assessment is a project. Ongoing assessments, remediation tracking, evidence management, and trend reporting are a service. vCIOToolbox gives your team a repeatable way to deliver compliance as a service across every client, so security becomes recurring value your clients see every quarter.
AI ASSISTANT FOR GRC
See the why behind every risk score, faster
The vCIOToolbox AI assistant pulls current information from every connected tool across your client portfolio in real time and adds business context to findings, so your vCISOs can explain risk in business speak, not tech speak.
CLIENT AND AUDITOR TRANSPARENCY
Reports clients understand and auditors trust
Easy-to-read reports show where risk exists and the steps to reduce it. In the read-only customer portal, clients see their assessment scorecard, strategic plan progress, and roadmap between meetings, so they watch their posture improve instead of hearing about it once a year.

Prepare your own MSP for the GTIA Cybersecurity Trustmark
The GTIA Cybersecurity Trustmark draws on controls from several established frameworks, carefully selected for what actually matters to MSPs and IT solution providers. Beyond the standards, it delivers prescriptive guidance and practical tools to support you at every stage of your cybersecurity journey.
What is vCISO software?
vCISO software is a platform that lets a virtual CISO, usually working at an MSP or MSSP, run security and compliance programs for many clients at once: framework assessments, risk registers, remediation plans, policies and evidence, and audit-ready reporting.
vCIOToolbox combines vCISO software with vCIO tools, so security findings flow into each client’s business reviews, roadmap, and budget.
What is a vCISO?
A vCISO (virtual chief information security officer) is an outsourced security leader who sets security strategy, runs risk and compliance programs, and advises leadership, usually part-time or on retainer. Many MSPs and MSSPs offer vCISO services to clients that need security leadership but can’t justify a full-time CISO.
What is compliance as a service?
Compliance as a service is a managed offering in which an MSP or MSSP runs a client’s compliance program on an ongoing basis: regular assessments against frameworks such as NIST CSF, CMMC, or HIPAA, remediation tracking, policy and evidence management, and audit preparation. vCIOToolbox gives MSPs one platform to deliver it consistently across every client.
Which compliance frameworks does vCIOToolbox support?
vCIOToolbox supports 35+ security, regulatory, and governance frameworks, including the NIST Cybersecurity Framework (CSF 2.0), NIST 800-171, CMMC, HIPAA, ISO 27001/27002, GDPR, IASME Cyber Essentials, CyberSecure Canada, COBIT, and many more. NIST assessments support maturity levels, so MSPs can move clients forward in practical stages
How is vCIOToolbox different from a standalone GRC or vCISO platform?
Standalone GRC and vCISO platforms stop at the assessment. vCIOToolbox connects security to the rest of the client relationship: findings become recommendations, recommendations become roadmap items with budgets, and progress shows up in every QBR. MSPs can run vCIO and vCISO services from one platform instead of paying for and reconciling two tools.
How does vCIOToolbox help MSPs sell security projects?
vCIOToolbox shows clients where their gaps are, what each finding means for the business, and how a remediation plan reduces risk, with the budget attached. When clients understand the impact, security stops being a cost they defer and becomes a decision they fund. vCIOToolbox customers report 30–60 day faster deal cycles.
How does the vCIOToolbox AI assistant help with compliance?
The vCIOToolbox AI assistant pulls current information from every connected tool across your client portfolio in real time and adds business context to findings, so vCISOs can see the why behind risk and assessment results faster and prepare compliance reviews in business language.
Your team reviews all AI-assisted content before any client sees it.
Can vCIOToolbox help my MSP prepare for the GTIA Cybersecurity Trustmark?
Yes. MSPs can use vCIOToolbox GRC to prepare for the GTIA Cybersecurity Trustmark, which draws controls from several established frameworks selected for MSPs and IT solution providers. Assessing your own practice first also gives your team a live example to show clients.